This Post belongs to Ruben he has posted in orkut..
PHP.Hop - PHP Honeypot Project
PHP HOP is an Opensource project
Application-based low-level interaction honeypot Dealing with web threats
widely in use to
Fool different kind of web attackers (audit tools, manual hax0rs...)
Create real statistics about the first top10 commands used by an intruder
Steal malware (PHP, C, Perl) that attackers wanted to upload
Identify evil behaviours and learn about current web threats
Live demo of a fake PHPShell module[http://webmail.rstack.org/config/]
More information about the project (PDF)[http://www.rstack.org/phphop/phphop.pdf]
Download current public version of PHP.HoP[http://www.rstack.org/phphop/download/]
Saturday, November 04, 2006


Upcoming changes in PHP 6.0
The PHP world is really excited about the upcoming release of PHP 6.0. Amongst all the uncertainties in any new release, PHP 6.0 seems to be getting rid of three of the earlier troublesome features: register_globals, magic_quotes_gpc and safe_mode. The first was a big security hole, the second messed with the data and made changing environments quite difficult, while the third was usually misread, and provided a false sense of security.
Ruben has updated in his blog.. long article.. please read it here
http://www.rubenbenjamin.com/blogs/?cat=4
Ruben has updated in his blog.. long article.. please read it here
http://www.rubenbenjamin.com/blogs/?cat=4
Thursday, September 28, 2006
Browser detection in PHP
Did you know that PHP has a built in function to detect which browser your visitor is running?
There is PHP’s get_browser function.
Here’s how to use this function:
< ? $visitorbrowser = get_browser(null,true); print_r($visitorbrowser); ?>
The output of this function is an object which contains details about the user’s browser and looks something like the one below:
[browser_name_regex] => ^mozilla/5.0 (windows; .*; windows nt 5.1.*) gecko/.* firefox/1.5.*$
[browser_name_pattern] => Mozilla/5.0 (Windows; *; Windows NT 5.1*) Gecko/* Firefox/1.5*
[parent] => Firefox 1.5
[platform] => WinXP
[browser] => Firefox
[version] => 1.5
[majorver] => 1
[minorver] => 5
[css] => 2
[frames] => 1
[iframes] => 1
[tables] => 1
[cookies] => 1
[backgroundsounds] =>
[vbscript] =>
[javascript] => 1
[javaapplets] => 1
[activexcontrols] =>
[cdf] =>
[aol] =>
[beta] =>
[win16] =>
[crawler] =>
[stripper] =>
[wap] =>
[ismobiledevice] =>
[netclr] =>
To get PHP to detect your browser properly, you’ll have to get the updated browsecap.ini file and set the path to the file in your php.ini file.
To set the path to browsecap.ini file, add the following entries in your php.ini file:
[browscap]
browscap = /path/to/browscap.ini
Links:
browsecap.ini file: http://browsers.garykeith.com/downloads.asp
PHP get_browser function lookup: http://in.php.net/manual/en/function.get-browser.php
Saturday, July 15, 2006
Tracking Yahoo User
Hi All,
I found the way how to track the yahoo user who is chatting with you.. Please follow the method as i have described below you can get his/her location like Country/State/City/Region and many more information..
simple method 1
make a simple script page in asp,php,jsp or any that logs in the remote user ip. then get the ip and do a query on whois.net.
you can get the geographical ip address.
simple method 2
send him an email and make him reply. check the headers.
all methods can give you his physical ip address and if is in a network you wont get his physical computer access.
if you want to get his ip for any sort of trojan attack/script attact etc.. this info isnt really useful.
By method 1 if he/she replies by the mail. In yahoo when you open the mail scroll down on right side you will find the Full header link click it the you will get all the information about the mail find the field [Received: from [202.80.49.75]] this is what the ip address copy this ip address then go to the site http://www.maxmind.com/app/locate_ip and paste the address and press the submit button you will get all the information.
For example:- i received the mail, then i clicked on Full header link i got the folowing information
X-Apparently-To: ansarahmed_8@yahoo.co.in via 203.84.221.31; Wed, 28 Jun 2006 21:19:01 +0530
X-Originating-IP: [209.191.86.236]
Return-Path:
Authentication-Results: mta117.mail.in.yahoo.com from=yahoo.com; domainkeys=pass (ok)
Received: from 209.191.86.236 (HELO web42103.mail.mud.yahoo.com) (209.191.86.236) by mta117.mail.in.yahoo.com with SMTP; Wed, 28 Jun 2006 21:19:00 +0530
Received: (qmail 33042 invoked by uid 60001); 28 Jun 2006 15:48:58 -0000
DomainKey-Signature: a=rsa-sha1; q=dns; c=nofws; s=s1024; d=yahoo.com; h=Message-ID:Received:Date:From:Subject:
To:MIME-Version:Content-Type:Content-Transfer-Encoding; b=KzThMRS6GXE1qm/driHDs9hZ1nylNPMAXvKR3EAVig8V6
+IAUuDYtpek1jtQHkTqRPYKZE
+7iGxuA1zWpjfSz8vjcDccm+i8T1PA4J9LpwYu/4k
+CbLDv9aqZL9Q4vEl3CgDCSn+
7PcI7HBoCqr3IsaEdeqGYaFL57i3ru6vp7Q= ;
Message-ID: <20060628154858.33040.qmail@web42103.mail.mud.yahoo.com>
Received: from [202.80.49.75] by web42103.mail.mud.yahoo.com via HTTP; Wed, 28 Jun 2006 08:48:58 PDT
Date: Wed, 28 Jun 2006 08:48:58 -0700 (PDT)
From: Send an Instant Message "h b" Add to Address BookAdd to Address Book
Yahoo! DomainKeys has confirmed that this message was sent by yahoo.com. Learn more
Subject: me (dont give to else)
To: ansarahmed_8@yahoo.co.in
MIME-Version: 1.0
Content-Type: multipart/mixed; boundary="0-1255100025-1151509738=:32596"
Content-Transfer-Encoding: 8bit
Content-Length: 6942
I found the received from field i.e Received: from [202.80.49.75].
When i copied and pasted this ip address
in http://www.maxmind.com/app/locate_ip i found all the information
Like Hostname,Country Name,City,State etc..
Regards,
Ansar Ahmed
I found the way how to track the yahoo user who is chatting with you.. Please follow the method as i have described below you can get his/her location like Country/State/City/Region and many more information..
simple method 1
make a simple script page in asp,php,jsp or any that logs in the remote user ip. then get the ip and do a query on whois.net.
you can get the geographical ip address.
simple method 2
send him an email and make him reply. check the headers.
all methods can give you his physical ip address and if is in a network you wont get his physical computer access.
if you want to get his ip for any sort of trojan attack/script attact etc.. this info isnt really useful.
By method 1 if he/she replies by the mail. In yahoo when you open the mail scroll down on right side you will find the Full header link click it the you will get all the information about the mail find the field [Received: from [202.80.49.75]] this is what the ip address copy this ip address then go to the site http://www.maxmind.com/app/locate_ip and paste the address and press the submit button you will get all the information.
For example:- i received the mail, then i clicked on Full header link i got the folowing information
X-Apparently-To: ansarahmed_8@yahoo.co.in via 203.84.221.31; Wed, 28 Jun 2006 21:19:01 +0530
X-Originating-IP: [209.191.86.236]
Return-Path:
Authentication-Results: mta117.mail.in.yahoo.com from=yahoo.com; domainkeys=pass (ok)
Received: from 209.191.86.236 (HELO web42103.mail.mud.yahoo.com) (209.191.86.236) by mta117.mail.in.yahoo.com with SMTP; Wed, 28 Jun 2006 21:19:00 +0530
Received: (qmail 33042 invoked by uid 60001); 28 Jun 2006 15:48:58 -0000
DomainKey-Signature: a=rsa-sha1; q=dns; c=nofws; s=s1024; d=yahoo.com; h=Message-ID:Received:Date:From:Subject:
To:MIME-Version:Content-Type:Content-Transfer-Encoding; b=KzThMRS6GXE1qm/driHDs9hZ1nylNPMAXvKR3EAVig8V6
+IAUuDYtpek1jtQHkTqRPYKZE
+7iGxuA1zWpjfSz8vjcDccm+i8T1PA4J9LpwYu/4k
+CbLDv9aqZL9Q4vEl3CgDCSn+
7PcI7HBoCqr3IsaEdeqGYaFL57i3ru6vp7Q= ;
Message-ID: <20060628154858.33040.qmail@web42103.mail.mud.yahoo.com>
Received: from [202.80.49.75] by web42103.mail.mud.yahoo.com via HTTP; Wed, 28 Jun 2006 08:48:58 PDT
Date: Wed, 28 Jun 2006 08:48:58 -0700 (PDT)
From: Send an Instant Message "h b"
Yahoo! DomainKeys has confirmed that this message was sent by yahoo.com. Learn more
Subject: me (dont give to else)
To: ansarahmed_8@yahoo.co.in
MIME-Version: 1.0
Content-Type: multipart/mixed; boundary="0-1255100025-1151509738=:32596"
Content-Transfer-Encoding: 8bit
Content-Length: 6942
I found the received from field i.e Received: from [202.80.49.75].
When i copied and pasted this ip address
in http://www.maxmind.com/app/locate_ip i found all the information
Like Hostname,Country Name,City,State etc..
Regards,
Ansar Ahmed
Saturday, July 01, 2006
How to Hack Yahoo ID ?
Hi Guys,
I was shocked when i heard one of my colleague yahoo id is hacked and its true we were receiving junk mails from that yahoo id and from day i was spending most of my free time to find out how they might have hacked her yahoo id. Then finally i got it how they might have hacked,The four most common ways of Hacking Yahoo ids are ..
1.) Social Engineering
2.) Password Crackers
3.) Using Password Stealing Trojans/Keyloggers
4.) Fake Login Pages
1. Social Enginnering is actually nothing but trying to know your personal and confidential details and then using it to change your password ..BUT HOW? ok there's a forgot password option with Yahoo which asks for your B'day,Country & Zip Code & later your security question..Now generally lamers who try this mode of Hacking have lots of time to waste ..They will put you into some kinda friendship/emotional trap and try to get all the above mentioned information .It may take 1-2 days or even 1-2 month ...(Really I pitty on such lamers !! ).
2.The second kinda Hacking attempt is done with the Help of Yahoo Password Crackers...I doubt bout their efficiency bt still some of them r lucky (other way round u r stupid lol)..Password Crackers & Password Changers use Brute Force Technique with their updated wordlists...WHAT IS BRUTE FORCE ?I'll make it simple ..it's like using all possible combinations and permutations on the available data and using it as a password ..Bt again it takes a hell lot of time to crack a password ....
3.The third and one of the most frequently used way of hacking or stealing Yahoo password is using trojans and keyloggers ..WHAT ARE TROJANS? hmmm.. I already have one ...bt still TROJANS are simple programs with a server part and the client part ..you infect the victims computer with the server part and the server then connects to the client running on your system and sends passwords and vital informations..and KEYLOGGERS are programs which record your keystrokes in a log.txt file and sends that log file to the Hacker...
I have this trojan programm beleive me it worked guys i tried it on my yahoo id. Dont want to say more about it secret ... lol.. ;) So please be carefull when you are accepting any files send by some one.
Once Infected by these trojans the infected server sends your password to the Hackers Yahoo Messenger id as PM 's ...
4. The last form of Yahoo Password stealing is done by using FAKE LOGIN PAGES ..Now wht the **** :-) is Fake login Page ?These are cloned pages of the real Yahoo Mail Sign in pages .They look very similar to the real conterparts and really very difficult to distinguish..Once you put inyour real id and password and press the submit button you will be either redirected to some other pasge /invalid login page but the trick had already been played by this time ..your id and password would have been mailed to the Hackers mail id by using a 3rd party SMTP server and you don't even realize that you are HACKED...
So be carefull Always view the address bar ..If the address bar shows something like http://mail.yahoo.com or http://edit.login.yahoo.com then its the authentic page but if its something different then DONOT login.
Friday, June 30, 2006
Global Include Trick
| As the major part in my PHP Application Architecture, this trick allows you to include a global file at the top of your scripts. It has the benefit of not keeping the file location or name inside of each individual PHP script. I was able to accomplish this by using Apache's SETENV directive. It registers a variable visible to all scripting languages through either an entry in either an .htaccess or httpd.conf file. Then in each of my PHP scripts I include that variable's contents. A very handy trick, if you ask me. |
Source: |
Monday, June 12, 2006
Creating a CAPTCHA with PHP
You may be thinking just exactly what is a captcha? Well you are likely to have already seen them across the web. They are those little images with a code on the front that you type into a box in order to submit something. This kind of system helps to prevent automatic submitting of an operation by some kind of program or robot. In this tutorial I will show you how to make a CAPTCHA just like the one below. Its not the most advanced captcha available because it uses a simple system font and nothing more.
The lines that you see above are to make any robots job of trying to work out that code a little harder. The dots in the background also help with this. Follow the link to learn more about how to create CAPTCHA.
The lines that you see above are to make any robots job of trying to work out that code a little harder. The dots in the background also help with this. Follow the link to learn more about how to create CAPTCHA.
Saturday, June 10, 2006
File Download Security
File Download Security
Want to prevent people from linking to your downloads? This script will force a page to be loaded before the download starts. HTML header statements are used to trigger the download of the file. PHP is used to push the file to the browser.
Principles
HTML headers must be sent before any output is sent to the browser. PHP uses the header function to pass raw HTML headers.
$dir="/path/to/file/";
if (isset($_REQUEST["file"])) {
$file=$dir.$_REQUEST["file"];
header("Content-type: application/force-download");
header("Content-Transfer-Encoding: Binary");
header("Content-length: ".filesize($file));
header("Content-disposition: attachment; filename=\"".basename($file)."\"");
readfile("$file");
} else {
echo "No file selected";
}
?>
We started with setting the directory where the files to be downloaded are located in $dir. Be sure not to use \ in $dir. Then we checked to make sure a filename was specified in the request. If a file was specified then we set $file to the path to the file and the filename. Now that the prep work is done its time to send the file to the browser.
The first header statement tells the browser to expect a download. The next two header statements tell the browser the format of the data and the size of the file respectively. The last header statement tells the browser the name of the file. Finally the readfile statement sends the file to the browser.
PHP User Group for Bangalore
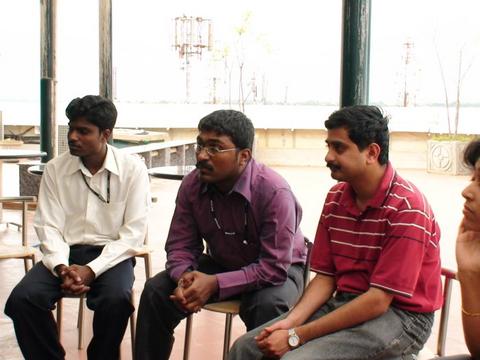
We had our very first Bangalore PHP meetup last Friday. We had a bunch of PHP people join up at our company terrace, to get the momentum going on meeting up PHP professionals around Bangalore. One of the key points at the discussion was to start a PHP user group in Bangalore, since there wasn’t one existing already (yep, the IT city doesn’t yet have a PHP user group). As a first step, we’ve setup a mailing list over at Yahoo groups to enable communication between the users. If you’re interested in joining the group, you can subscribe bang-phpug-subscribe@yahoogroups.com. This is still a new group so we’re still getting the momentum going with discussions and memberships, so do contribute to the discussions over at the group.
Check the following meetup.com page regarding the meeting:
http://php.meetup.com/329/
Subscribe to:
Posts (Atom)


 Posts

